The modern threat landscape is relentless. Gone are the days when a simple firewall and an antivirus subscription were enough to keep the digital wolves at bay. Today's cyber threats—ranging from sophisticated ransomware campaigns to zero-day exploits and AI-driven social engineering—target organizations of every size and sector.
For the IT department, this shift changes everything. Security can no longer be treated as an afterthought or bolted on as an auxiliary feature; it must be woven into the very DNA of organizational infrastructure. But how can IT teams, often stretched thin between helpdesk tickets and system upgrades, effectively manage and mitigate these escalating threats?
Here is a blueprint for how IT departments can move from a reactive firefighting mode to a proactive posture of digital resilience.
1. Shift from Perimeter Defense to Zero Trust
Traditional security models relied on a "castle-and-moat" philosophy: once you were inside the corporate network, you were largely trusted. In a world of remote work, cloud adoption, and BYOD (Bring Your Own Device) policies, that perimeter has effectively dissolved.
IT departments must champion a Zero Trust architecture. The core principle is simple: Never trust, always verify. Every user, device, and application attempting to access corporate resources must be authenticated, authorized, and continuously validated—regardless of whether they are sitting in the headquarters or logging in from a coffee shop halfway across the world.
2. Automate Threat Intelligence and Incident Response
Human error and fatigue are a security team's greatest vulnerabilities. When an alert fires at 2:00 AM, waiting for a human analyst to manually parse logs can mean the difference between a minor blip and a catastrophic breach.
Modern IT departments must leverage automated Security Information and Event Management (SIEM) and Extended Detection and Response (XDR) tools. Automation allows teams to:
Isolate compromised endpoints instantly.
Block suspicious IP addresses in real time.
Prioritize genuine threats from background noise, allowing human experts to focus on complex investigation and remediation.
3. Transform Employees from Liabilities to Assets
The human element remains the most targeted vector for cybercriminals. Phishing emails have evolved from obvious scams riddled with typos into hyper-personalized, convincing communications often enhanced by generative AI.
Training cannot be an annual compliance checkbox consisting of a boring 30-minute video. IT departments must foster a security-first culture through:
Continuous, engaging micro-training: Short, relevant lessons delivered regularly.
Unannounced phishing simulations: Realistic testing that helps employees spot red flags safely.
A "blameless" reporting culture: Encouraging staff to report accidental clicks or suspicious emails immediately without fear of punishment. Speed of reporting is critical to containment.
4. Implement Rigorous, Immutable Backups
When ransomware strikes, the ultimate insurance policy is a clean, recoverable backup. However, sophisticated attackers now actively seek out and destroy online backup repositories before launching their payload.
IT teams must adhere to the 3-2-1-1 backup rule:
3 copies of your data (1 primary and 2 backups).
2 different storage media types.
1 copy stored offsite.
1 copy stored immutably (offline or in a write-once-read-many state that cannot be altered or deleted by ransomware).
Regular disaster recovery drills are equally essential. A backup is only as good as its restoration time.
5. Embrace Continuous Vulnerability Management
Waiting for scheduled annual penetration tests leaves windows of opportunity wide open for attackers. The vulnerabilities database grows daily, and patches must be deployed with equal agility.
IT departments should establish continuous vulnerability scanning integrated with automated patch management workflows. Critical patches for operating systems, firmware, and third-party software should be triaged and applied swiftly, balancing system stability with urgent risk mitigation.
Suggested Blog Image Concept
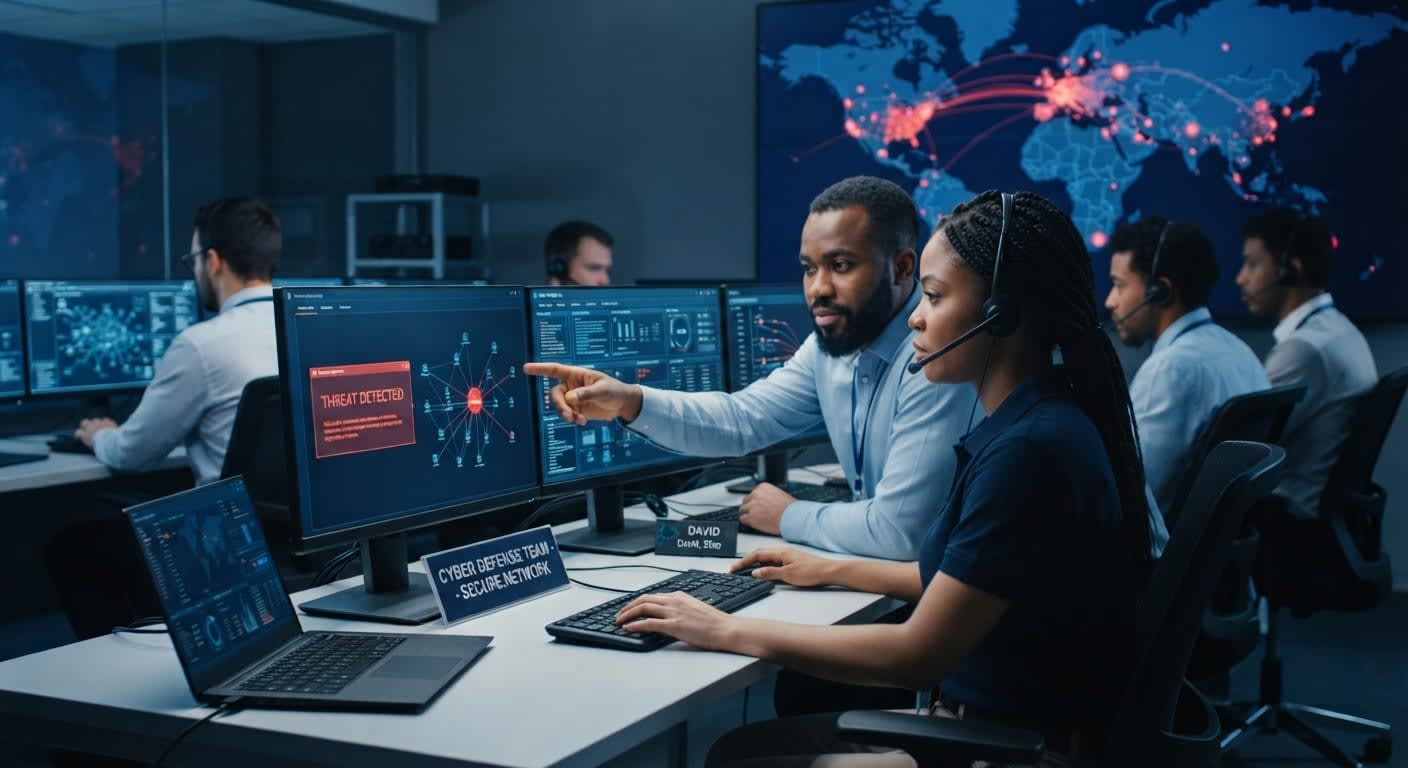
Visual Description: A sleek, high-tech abstract illustration depicting a glowing digital network shield being reinforced by diverse IT professionals working collaboratively. Cool blue and teal tones dominate the background, accented by vibrant amber highlights representing active threat monitoring nodes on a holographic dashboard.
Suggested Alt Text: Abstract digital illustration of an IT security shield and network monitoring dashboard.
Conclusion
Securing the enterprise against modern cyber threats is not about achieving absolute invulnerability—that is an impossible standard. Rather, it is about building resilience, minimizing the "blast radius" of potential incidents, and ensuring that the organization can detect, contain, and recover with minimal disruption. By adopting a proactive stance, empowering staff, and leveraging automation, the IT department can transform itself from a cost center into the ultimate guardian of enterprise trust.
Comments
Be the first to comment.
Leave a Comment